DMARC Record: Examples and How to Set It Up
What a DMARC record is, 5 copy-ready examples, every tag explained and a safe path from p=none to p=reject. Updated for the new DMARC standard, RFC 9989.

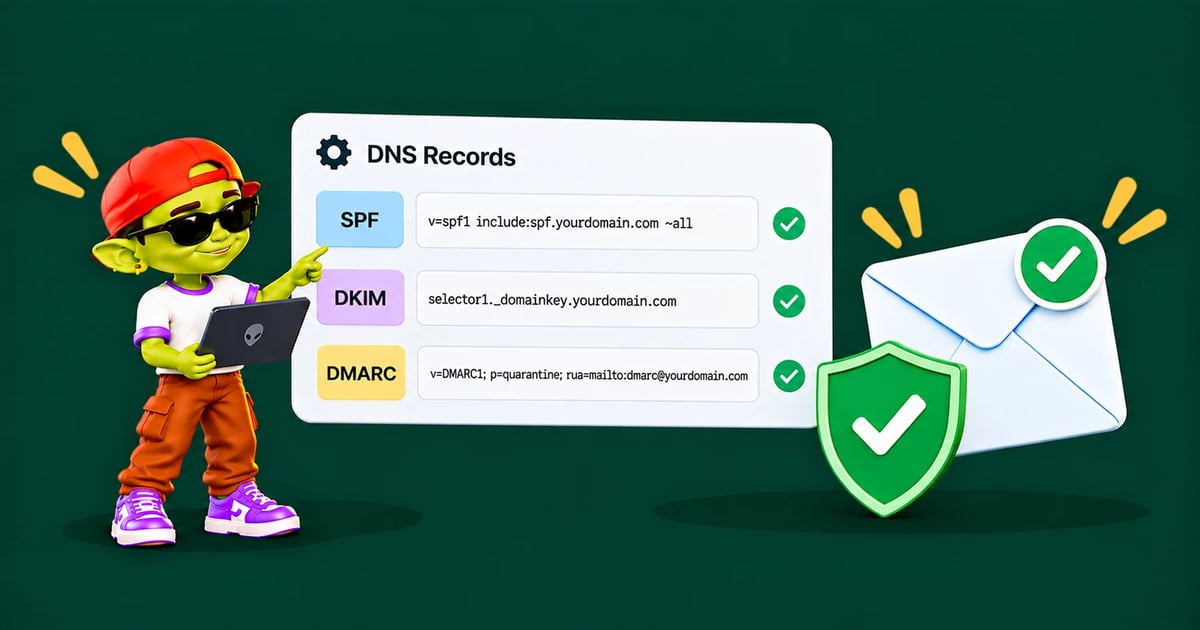
The short answer: A DMARC record is a TXT record at _dmarc.yourdomain.com that tells mailbox providers what to do with email that fails SPF and DKIM checks, and where to send reports. Start with
v=DMARC1; p=none; rua=mailto:[email protected], read the reports for a few weeks, then move to p=quarantine and p=reject.
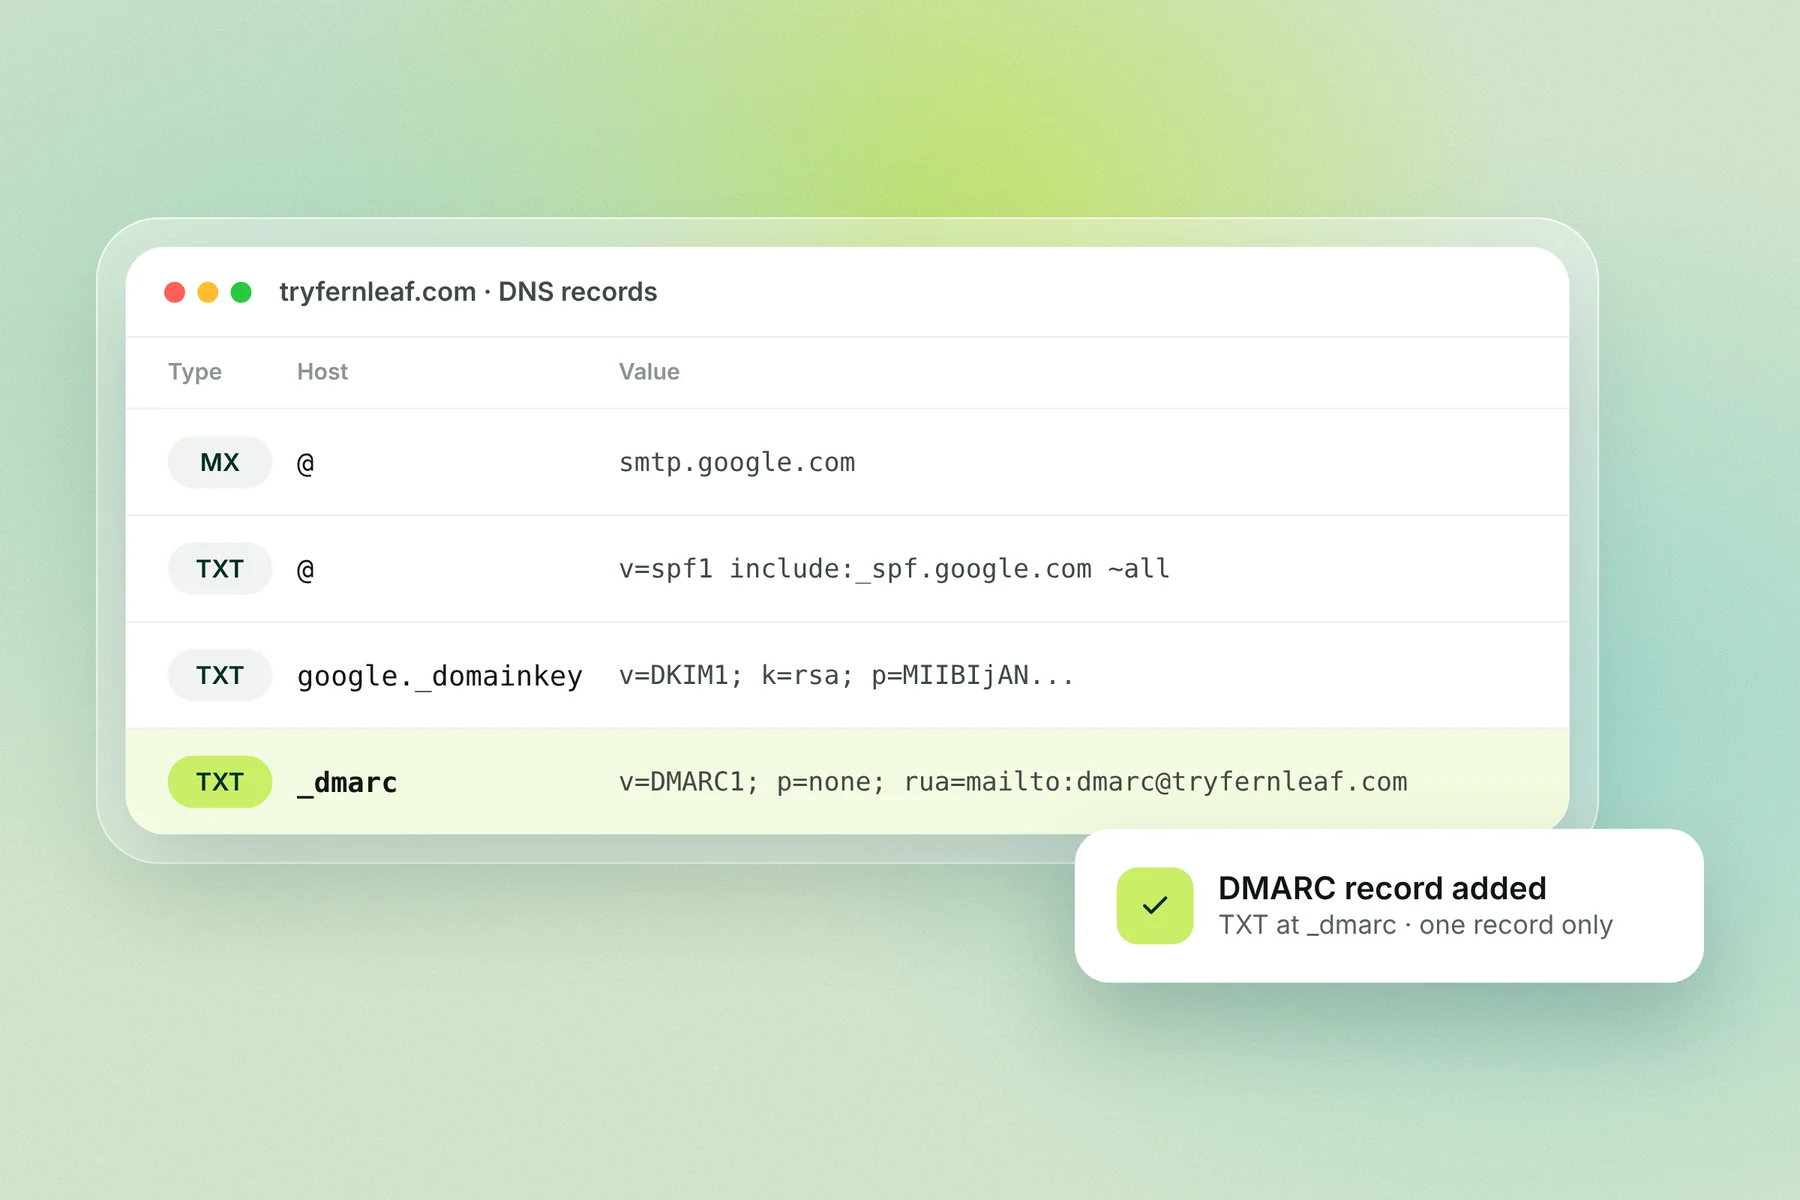
What a DMARC record does
DMARC checks that the domain in your From: address matches a domain that passed SPF or DKIM. That match is called alignment. Your DMARC record then tells the receiving server what to do when the check fails, and where to send daily reports about who is sending email as your domain.
It does 3 jobs:
Stops spoofing. At p=quarantine or p=reject, email that fakes your domain goes to spam or is refused.
Shows you every sender. Aggregate reports list each server sending as your domain, and whether it passed.
Meets Gmail and Yahoo's rules. Both require DMARC from bulk senders, and p=none is enough to meet that.
DMARC record examples you can copy
Replace tryfernleaf.com with your domain and the report address with a mailbox you read.
1. Start here: monitor only
v=DMARC1; p=none; rua=mailto:[email protected]Nothing changes for your email. You start getting reports.
2. Send failing email to spam
v=DMARC1; p=quarantine; rua=mailto:[email protected]3. Refuse failing email
v=DMARC1; p=reject; rua=mailto:[email protected]4. Cover subdomains, including ones that don't exist
v=DMARC1; p=reject; sp=reject; np=reject; rua=mailto:[email protected]The np tag is new in RFC 9989. It sets the policy for subdomains that don't exist, a common target for spoofers.
5. A cold email sending domain
v=DMARC1; p=none; rua=mailto:[email protected]; adkim=r; aspf=rRelaxed alignment (r) is the default, so adkim=r and aspf=r only make it explicit. Relaxed lets mail signed by mail.tryfernleaf.com align with tryfernleaf.com.
DMARC tags explained
Only v and p are needed; v must come first. Tags are separated by semicolons.
Tag | What it does | Values | Default | Status in RFC 9989 |
|---|---|---|---|---|
v | Version | DMARC1 | Required, first | Current |
p | Policy for your domain | none, quarantine, reject | Treated as none if missing | Current |
sp | Policy for subdomains | none, quarantine, reject | Same as p | Current |
np | Policy for subdomains that don't exist | none, quarantine, reject | Falls back to sp, then p | New |
rua | Where daily aggregate reports go | mailto: address | No reports | Current |
ruf | Where failure reports go | mailto: address | No reports | Current |
adkim | DKIM alignment | r (relaxed), s (strict) | r | Current |
aspf | SPF alignment | r (relaxed), s (strict) | r | Current |
fo | When to send failure reports | 0, 1, d, s | 0 | Current |
t | Test mode | y, n | n | New |
psd | Marks a public suffix domain | y, n, u | u | New (registries only) |
pct | Share of failing mail the policy applies to | 0 to 100 | 100 | Historic (deprecated) |
rf, ri | Report format and interval | afrf; seconds | afrf; 86400 | Historic (deprecated) |
What changed in 2026: RFC 9989
On 19 May 2026 the DMARC standard moved from RFC 7489, an informational document from 2015, to RFC 9989, a full Internet standard. Two companion standards, RFCs 9990 and 9991, cover the reports. For most senders, a record that works today keeps working.
The changes that matter:
pct is historic. RFC 9989 lists pct, rf and ri as "historic", meaning deprecated. Don't build a rollout on pct=10 or pct=50.
t is the new test mode. t=y asks receivers not to apply your policy fully; RFC 9989 says the owner expects "one level below the specified policy", so p=quarantine with t=y acts like p=none.
np covers made-up subdomains. Spoofers often invent subdomains such as billing.yourdomain.com; np sets the policy for those.
Two records still means none. If a receiver finds more than one DMARC record, "they are all discarded".
Support for the new tags will take time to spread, so the safest records still use only v, p, sp and rua. It isn't yet clear which major mailbox providers honor t and np; neither RFC says.
p=none vs p=quarantine vs p=reject
The p tag decides what happens to email that fails DMARC. Start at none, and move up only when your reports show every real sender passing.
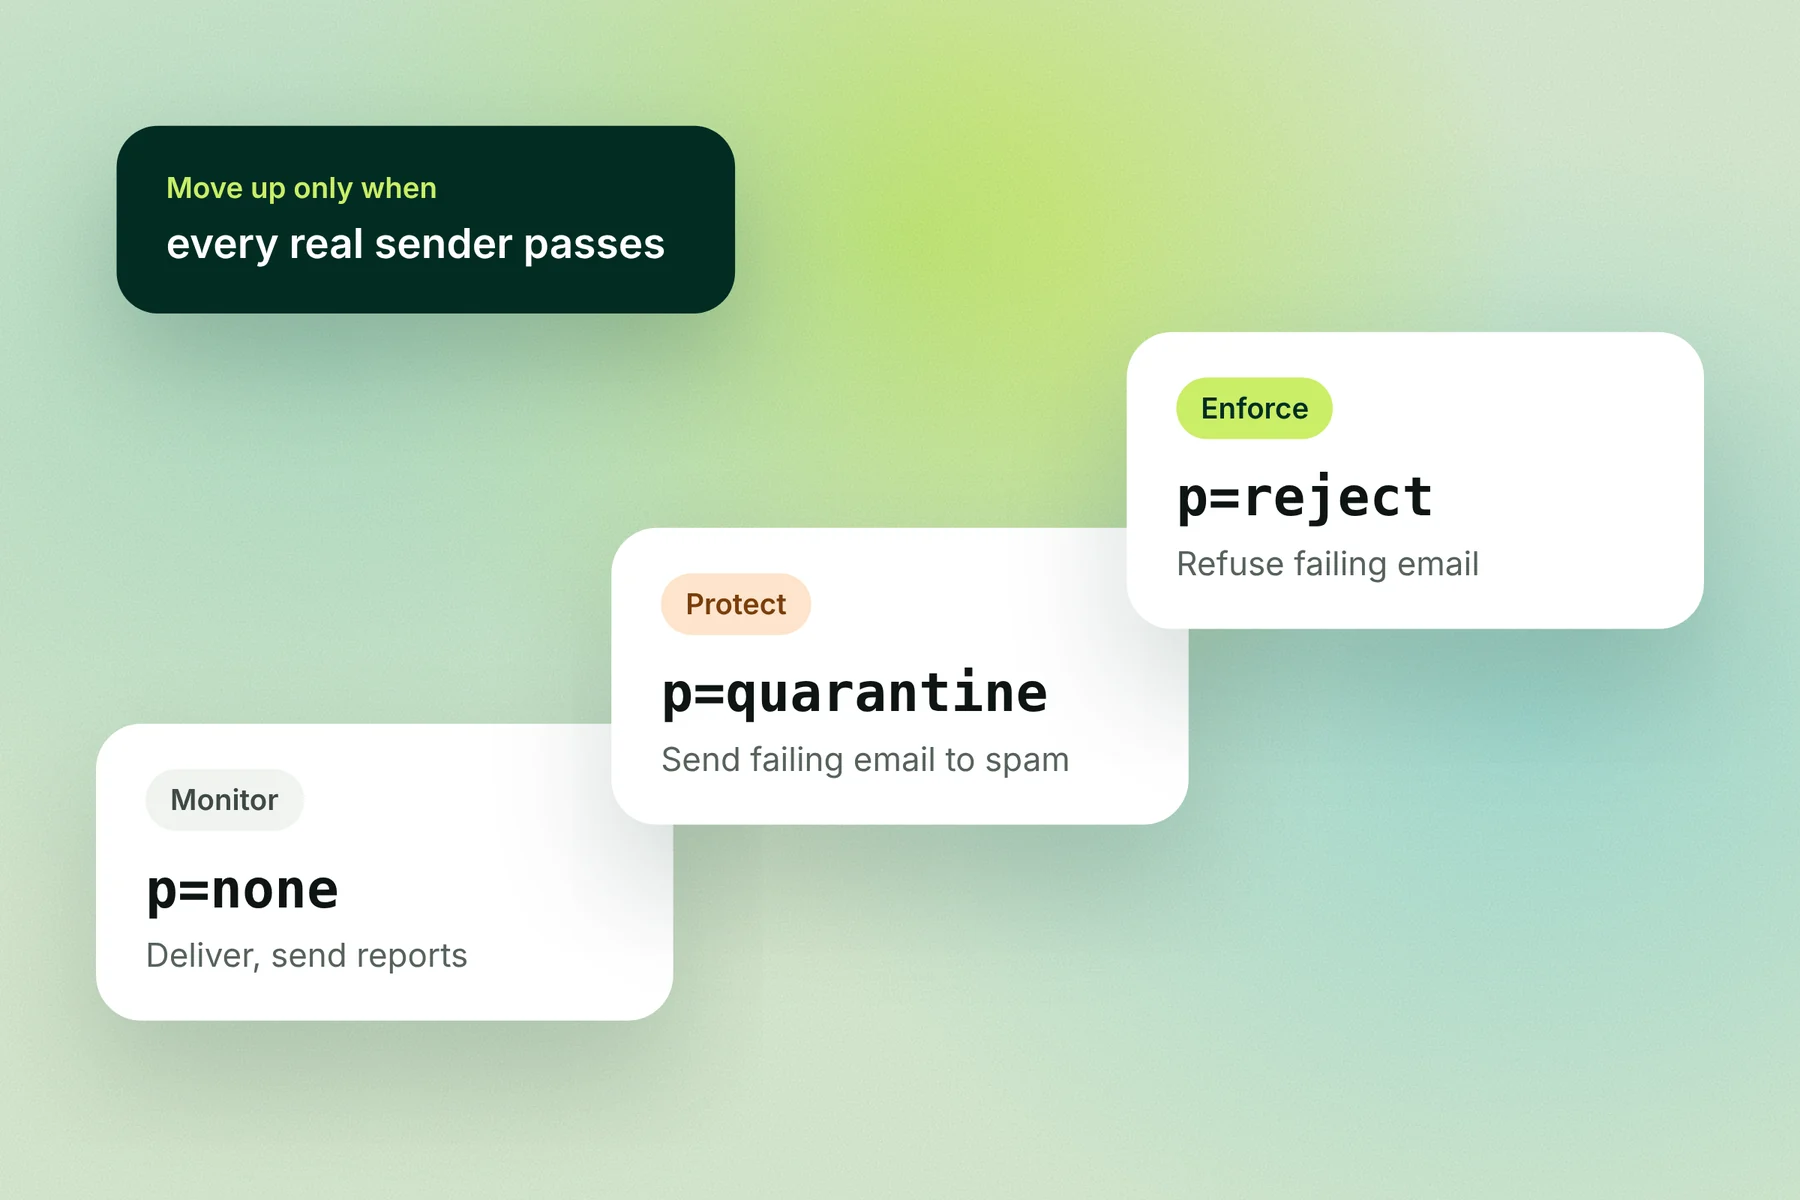
Policy | What happens to failing email | Stops spoofing? | Use it when |
|---|---|---|---|
p=none | Delivered as normal; you get reports | No | First weeks, while you find every sender |
p=quarantine | Treated as suspicious, usually sent to spam | Mostly | Every real sender passes in your reports |
p=reject | Refused, ideally before it's accepted | Yes | Quarantine has run without real email failing |
p=none meets Gmail and Yahoo's bulk sender rule but doesn't protect your domain. Treat it as a starting point, not the finish line.
How to add a DMARC record (any DNS provider)
Adding the record takes about 5 minutes. Set up SPF and DKIM first, because DMARC passes only when one of them passes and aligns.
Check SPF and DKIM. Both should already pass for every service that sends as your domain. See SPF, DKIM and DMARC explained.
Open your DNS settings at the company that hosts your domain's DNS (often your registrar, or Cloudflare).
Add a TXT record with these values:
Field | Value |
|---|---|
Type | TXT |
Host / Name | _dmarc (some providers want _dmarc.tryfernleaf.com) |
Value | v=DMARC1; p=none; rua=mailto:[email protected] |
TTL | Default (often 3600 seconds) |
Save, then wait. Most changes show within the record's TTL, often under an hour.
Check it with a DMARC lookup (next section).
Repeat for every domain that sends email, including each secondary cold email domain.
If a DMARC record already exists, edit it. Never add a second one.
A safe rollout plan
Move up one step at a time, and only when the reports are clean.
Step | Record | Move on when |
|---|---|---|
1. Monitor | p=none; rua=... | Reports show every real sender, usually after 2 to 4 weeks |
2. Fix | Same record | Every real sender passes SPF or DKIM with alignment |
3. Quarantine | p=quarantine; rua=... | 2 to 4 weeks with no real email failing |
4. Reject | p=reject; rua=... | Keep it, and keep reading reports |
The week counts are a common rule of thumb, not part of the standard. Under RFC 9989, use t=y if you want a test step instead of the old pct.
Who requires DMARC
Mailbox provider | Who must have DMARC | Minimum policy | Since |
|---|---|---|---|
Gmail | Bulk senders: 5,000+ messages a day to personal Gmail accounts | p=none | 1 Feb 2024 |
Yahoo | Bulk senders | p=none, with relaxed alignment allowed | Not stated on its page |
Outlook.com, Hotmail, Live | More than 5,000 emails a day to Outlook.com | p=none, aligned with SPF or DKIM | 5 May 2025 |
Below the bulk line, Gmail asks for SPF or DKIM only, and Yahoo "strongly urges all senders" to publish DMARC. For cold email, set it up on every sending domain anyway: it's free, and it shows you who sends as your domain.
How to check your DMARC record
Look up the TXT record at _dmarc.yourdomain.com. A good result shows exactly one record that starts with v=DMARC1 and has a valid p tag.
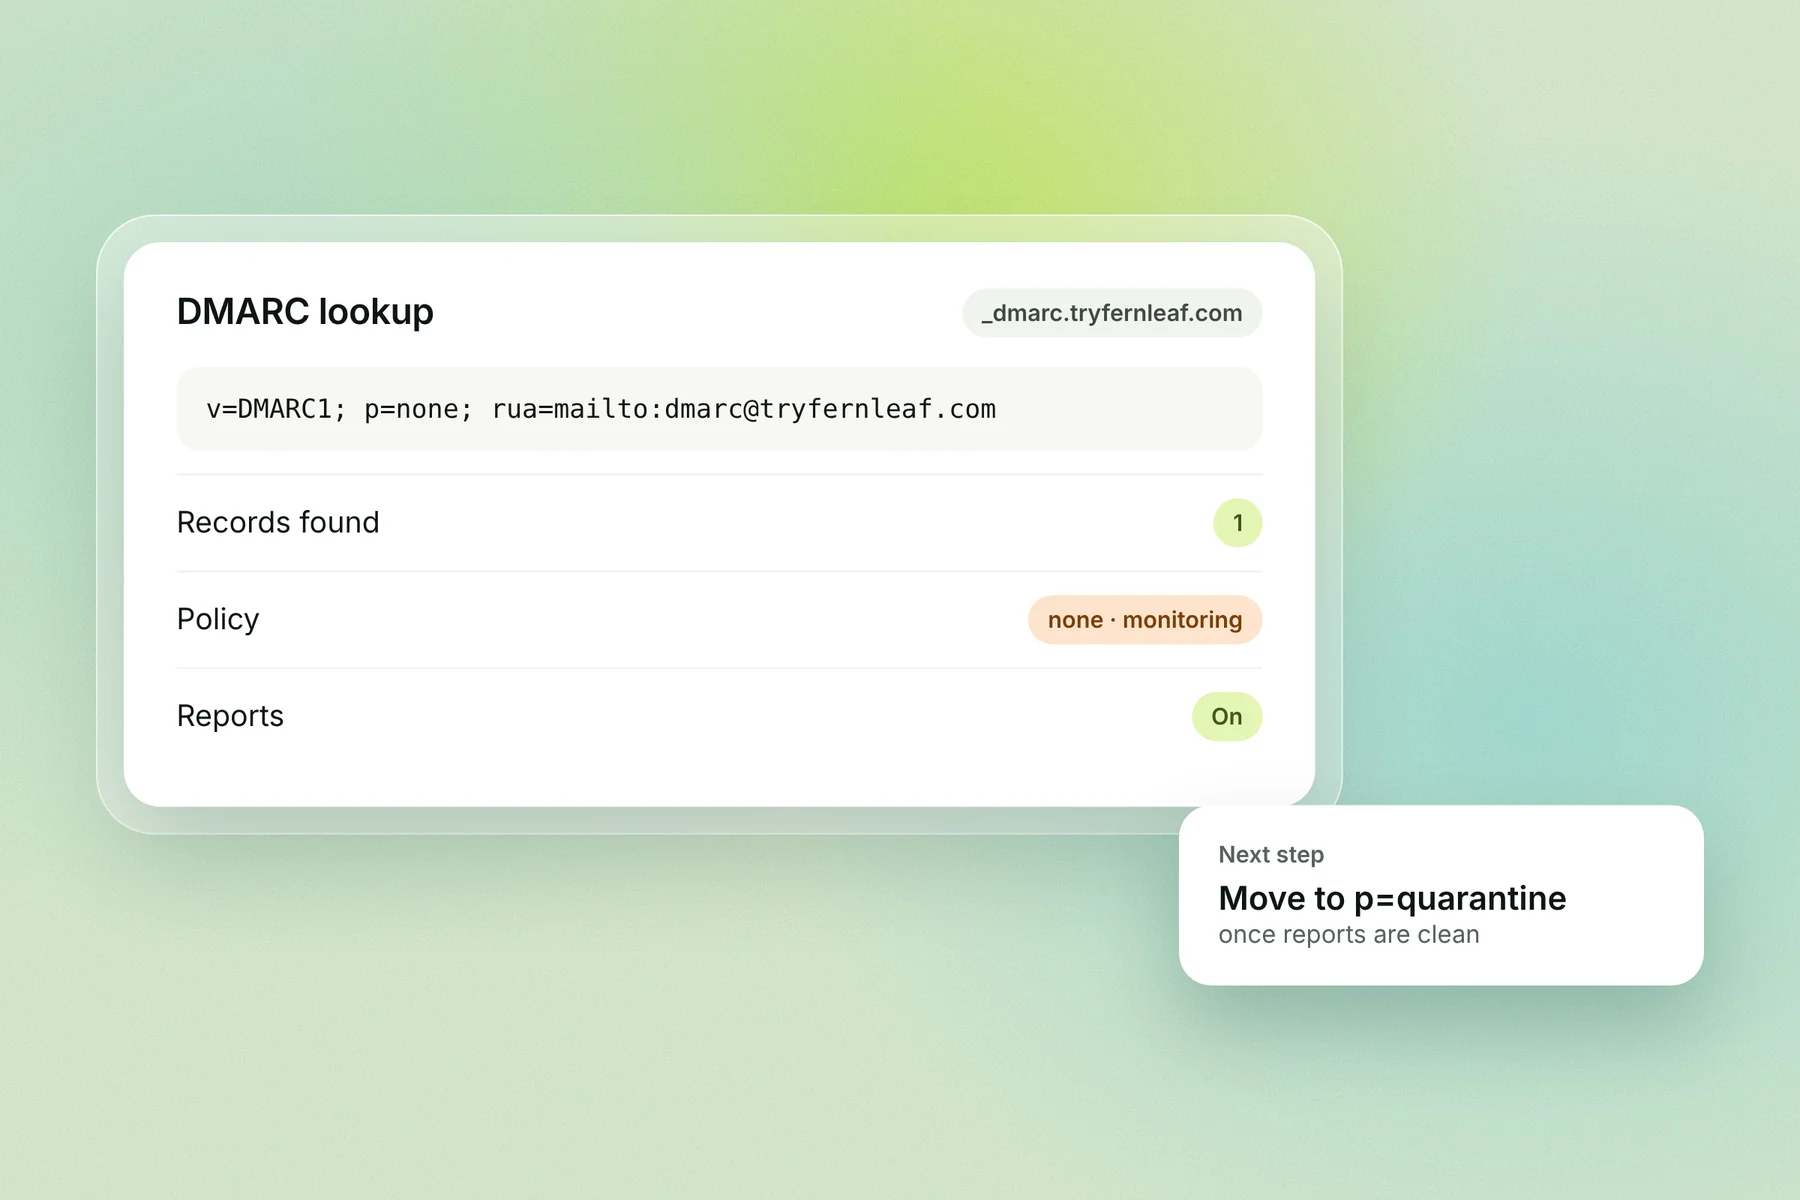
Command line:
dig TXT _dmarc.tryfernleaf.com +short(Mac and Linux) ornslookup -type=TXT _dmarc.tryfernleaf.com(Windows)In an email: open a message you sent, view the original or headers, and find
dmarc=passin the Authentication-Results lineOnline: any DMARC lookup tool, such as MXToolbox's
What to look for: one record only, v=DMARC1 first, a p value, and a report address you actually read.
How to read DMARC reports
Aggregate reports arrive as XML files, usually once a day from each large mailbox provider, at your rua address. Each one lists the servers that sent email as your domain, how many messages they sent, and whether SPF, DKIM and alignment passed.
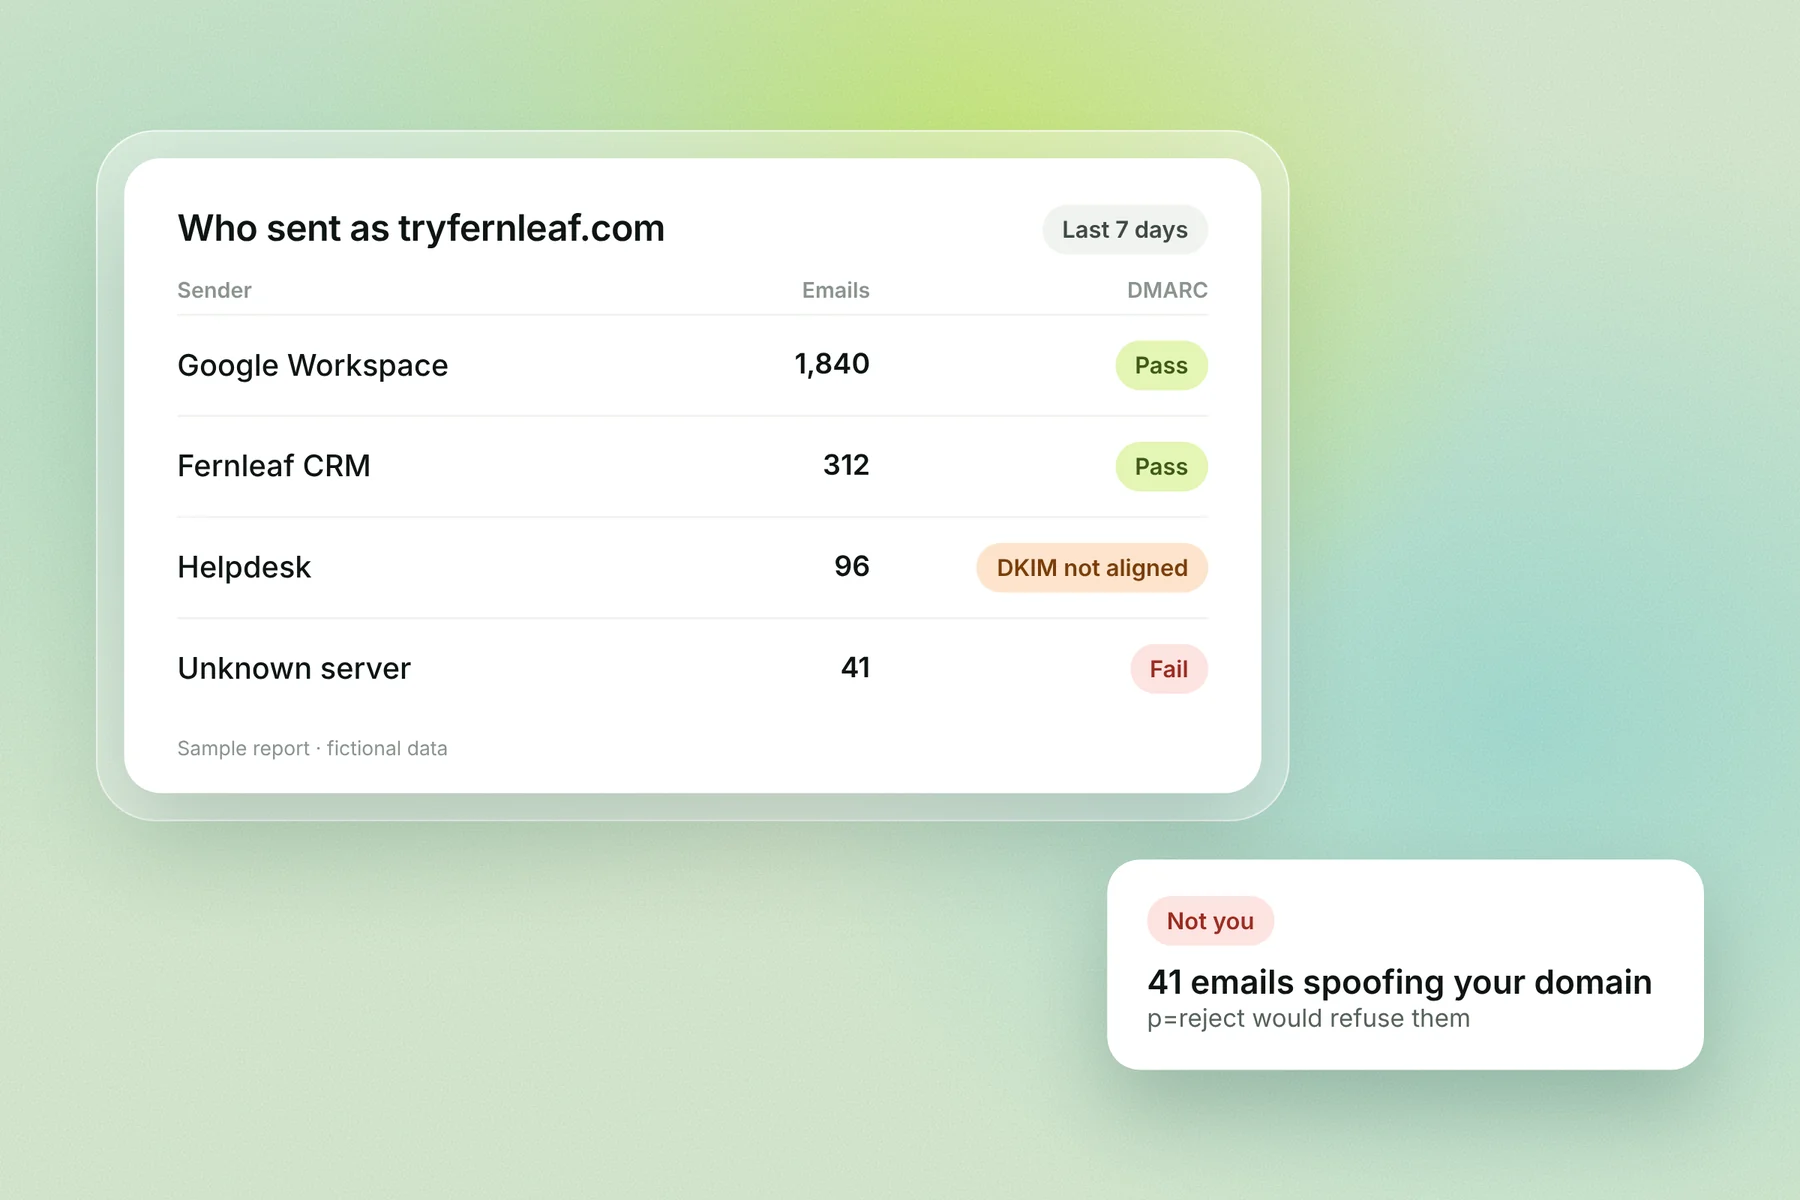
Raw XML is hard to read, so most people send rua to a free or paid report reader. Look for 3 things:
A real sender failing, such as your CRM or helpdesk. Fix its SPF or DKIM before moving past p=none.
Unknown servers sending as you. That's spoofing, and the reason to reach p=reject.
Alignment failures with SPF or DKIM passing. The service is signing with its own domain; set up custom DKIM with your domain.
Common DMARC mistakes
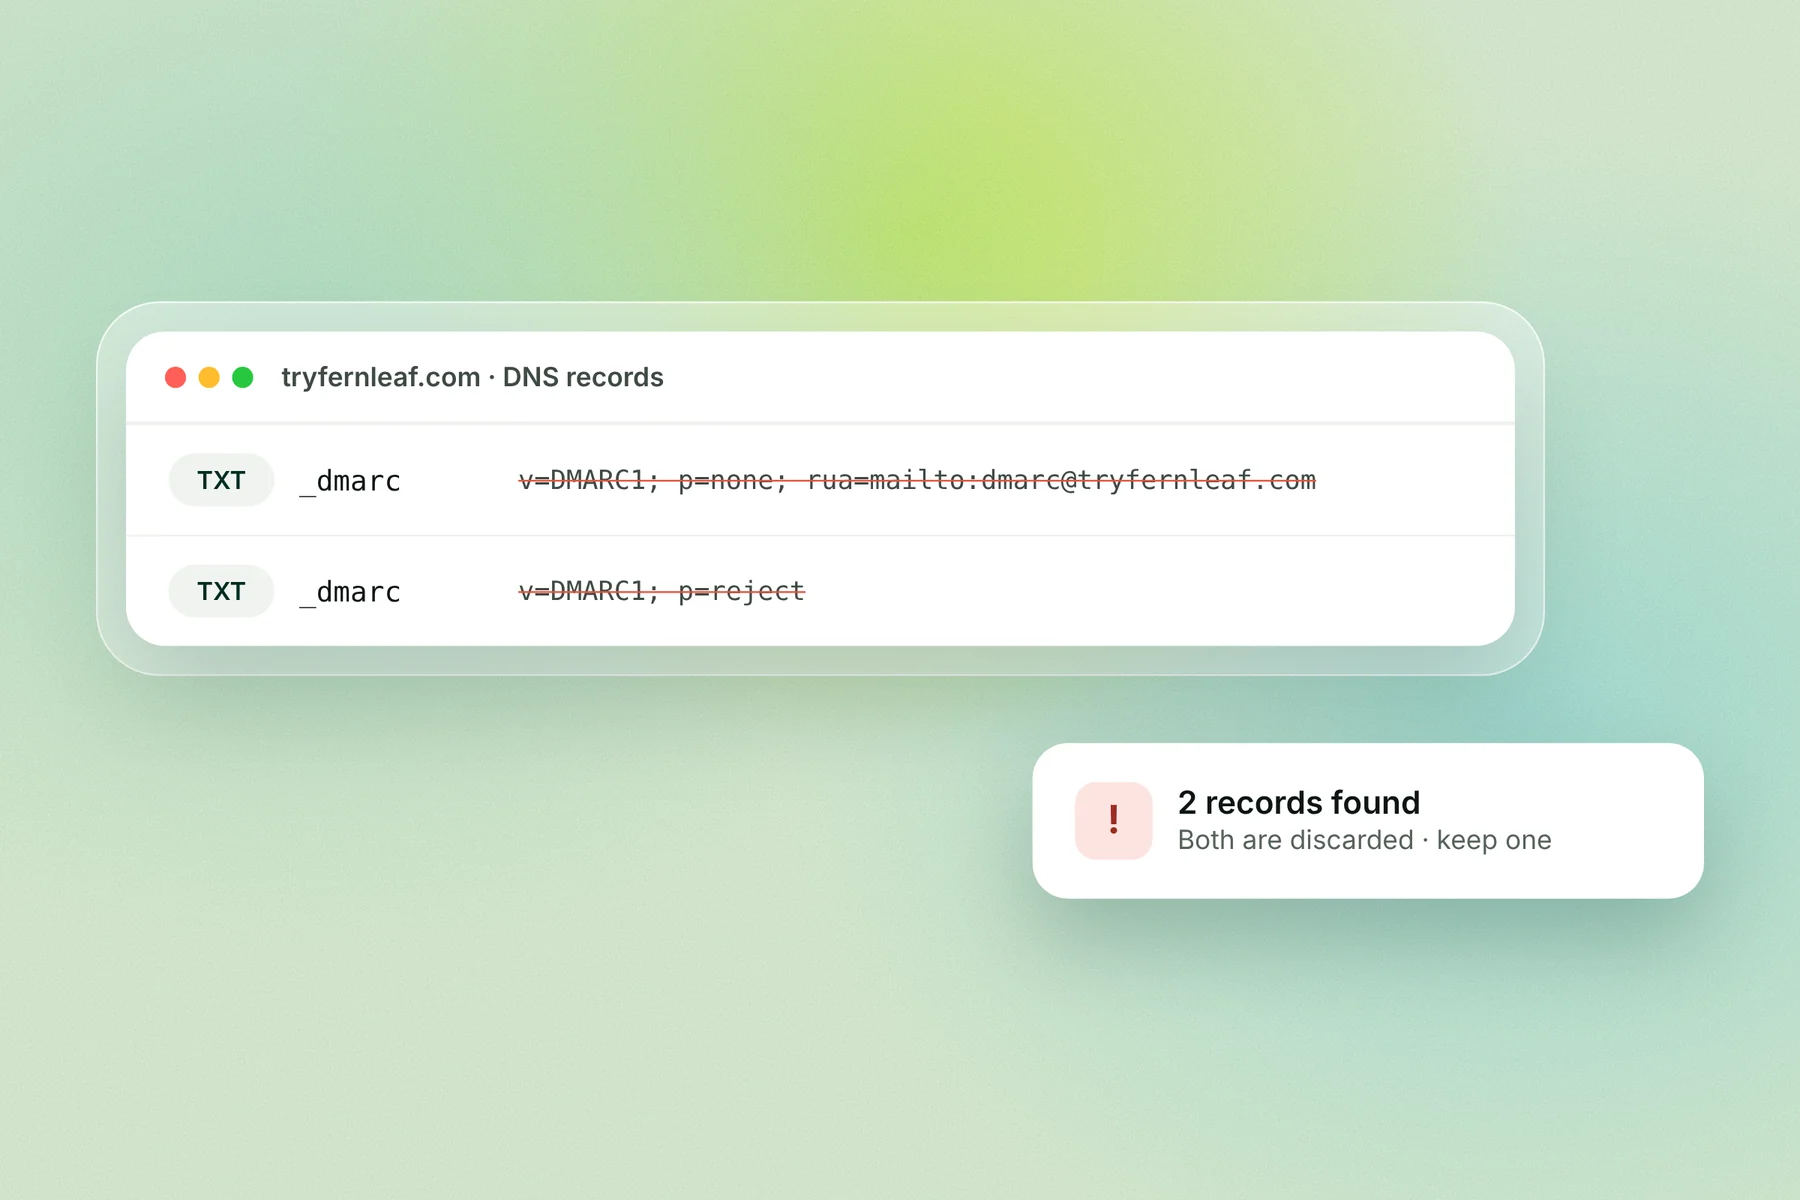
Two DMARC records. Receivers discard both, so you have no DMARC at all. Keep one and edit it.
Record at the wrong host. It must be at _dmarc, not at the root (@) of the domain.
Stopping at p=none. It meets the bulk sender rule but doesn't stop spoofing.
Jumping to p=reject on day 1. Any real sender you missed gets its email refused.
No rua address. Without reports you can't see what's failing.
Relying on pct. It's historic under RFC 9989; move up the policy ladder instead.
Forgetting secondary domains. Each cold email domain needs its own record.
Check your setup with Alien Mail
Alien Mail checks SPF, DKIM and DMARC on every domain you connect and tells you which record is missing before you send. Warmup is free on every inbox, and you pay only per email sent. Start free with 100 credits and no card.
Start free → · How Alien Mail handles deliverability
Frequently asked questions
What is a DMARC record? A TXT record at _dmarc.yourdomain.com that tells receiving servers what to do with email failing SPF and DKIM alignment, and where to send reports.
What is a good first DMARC record? v=DMARC1; p=none; rua=mailto:[email protected]. It changes nothing about delivery and starts daily reports.
Is p=none enough? It meets Gmail and Yahoo's bulk sender rule, but it doesn't stop anyone spoofing your domain. Move to p=quarantine and then p=reject once reports are clean.
Can I have two DMARC records? No. Under RFC 9989, if more than one DMARC record is found, "they are all discarded", so you end up with no DMARC.
Is the pct tag still used? RFC 9989, the 2026 DMARC standard, lists pct as historic. Use the t tag for testing, and move up the policy ladder instead of using percentages.
Do cold email domains need DMARC? Yes. Gmail and Yahoo require it from bulk senders, and a record on every sending domain lets you see and fix failures early.
How long does a DMARC record take to work? Usually within the record's TTL, often under an hour. Reports start once providers have seen your email, typically within a day or two.
Key terms
DMARC: a standard that checks the From: domain matches a domain that passed SPF or DKIM, and tells receivers what to do if not.
Alignment: the From: domain matching the SPF or DKIM domain, exactly (strict) or by organizational domain (relaxed).
Policy (p): what to do with failing email: none, quarantine or reject.
Aggregate report (rua): a daily XML summary of who sent email as your domain and whether it passed.
RFC 9989: the 2026 DMARC standard that replaced RFC 7489.